The top five web application-specific attack surface management opportunities Sprocket Security sees regularly.
Resources
Blog
Web App Assessments
Keep up to date with the latest offensive security news, knowledge, and resources.
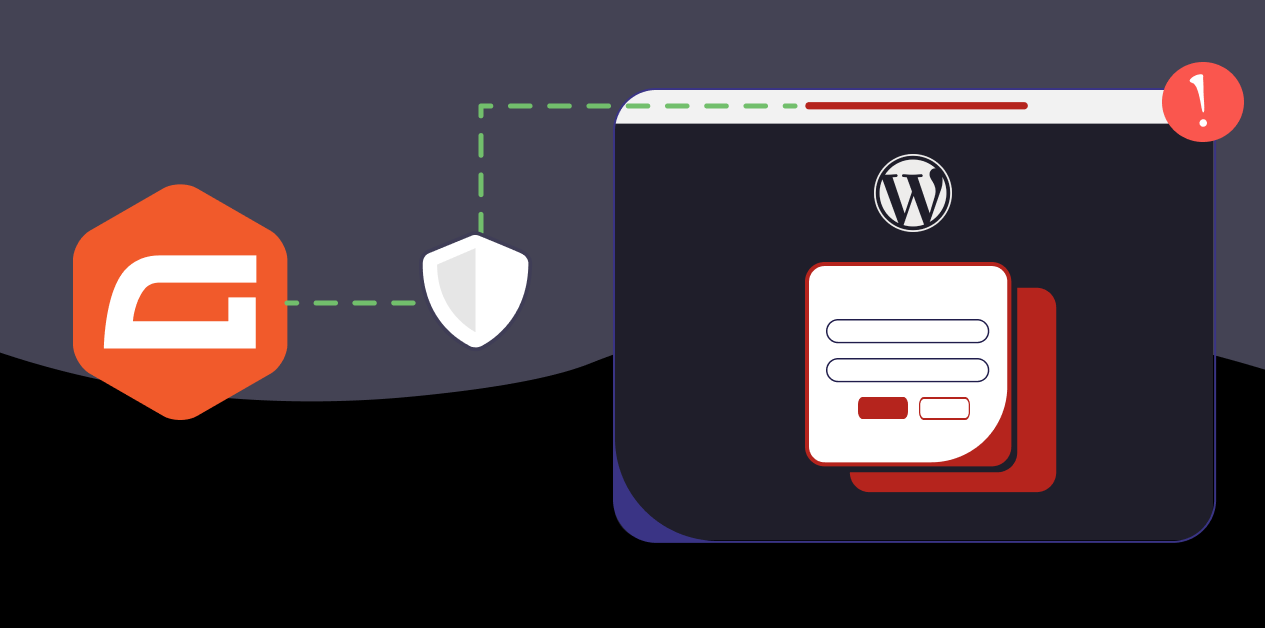
By targeting a specific endpoint and passing in a random string, GravityForms will prompt users to authenticate first. This results in the unauthenticated user being redirected to the obscured administrative login page for /wp-admin.

Did you know you can interact with LDAP using cURL? How about NTLM, proxy tunneling, or domain sockets?
A deep dive into some less common and advanced features of cURL, including sending POST requests with a payload file, uploading files to a server, exploiting Spring4Shell, and exploiting SQL injection vulnerabilities using cURL.

Exploiting several Top 10 risks using the Damn Vulnerable Web Application (DVWA), as it’s expressly configured to highlight sub-optimal cybersecurity practices relevant to modern web applications.
